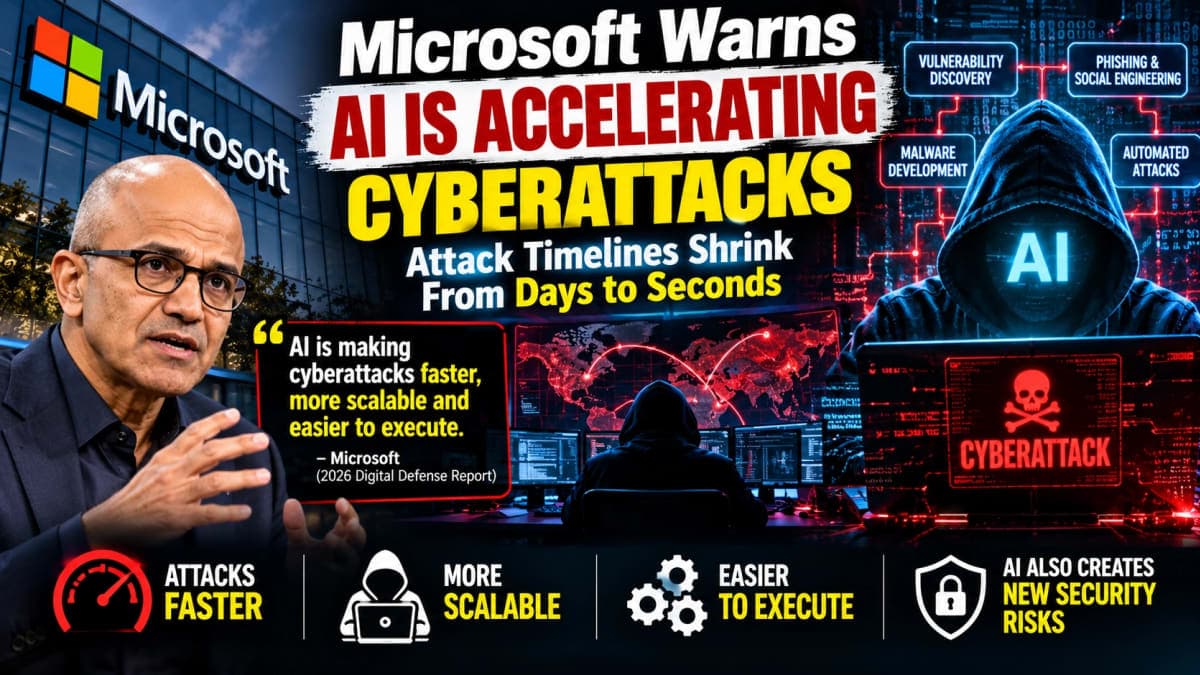
October 3, 2026: Artificial intelligence is changing the speed and scale of cyberattacks, allowing threat actors to automate parts of operations that previously required considerably more time and technical effort, according to Microsoft's newly released 2026 Digital Defense Report.
Microsoft says attackers are incorporating AI into reconnaissance, vulnerability discovery, social engineering, malware and exploit development, and post-compromise activity. In some areas, automation can compress portions of an attack chain from days to seconds.
However, Microsoft's findings do not suggest that AI has replaced conventional hacking techniques. People, stolen credentials, exposed systems and trusted access remain major entry points. Instead, AI is increasingly functioning as an accelerator for existing attack methods.
AI Is Changing the Speed of Cyberattacks
The central message of Microsoft's 2026 report is that cybersecurity is becoming a race increasingly conducted at machine speed.
AI tools can help attackers search software for weaknesses, tailor social-engineering campaigns, develop malicious code and automate portions of an intrusion. Microsoft says sophisticated capabilities are becoming more accessible while attack timelines are shrinking.
Vulnerability discovery is a particularly important example. Nearly 40,000 Common Vulnerabilities and Exposures (CVEs) were published during the first half of 2026, according to Microsoft. The company says AI-assisted code analysis can help both security researchers and attackers identify weaknesses more efficiently.
That creates a difficult dynamic: the same technology that helps defenders discover vulnerabilities before they are exploited can also help attackers search for weaknesses.
Cybercriminals Are Using AI Across the Attack Chain
Microsoft's threat intelligence teams have observed malicious actors incorporating AI into several stages of cyber operations, including reconnaissance, phishing and impersonation, vulnerability research, malware and exploit development, and activity after an initial compromise.
The company previously documented how threat actors were operationalising AI throughout the cyberattack lifecycle, using both ordinary model capabilities and attempts to circumvent model safeguards.
The significance is therefore less about AI creating entirely new forms of cybercrime and more about its potential to make established techniques faster, cheaper, more scalable and easier to personalise.
AI Agents Add Another Layer of Risk
Microsoft is particularly focused on the emergence of agentic AI—systems capable of interacting with applications, APIs, data and tools and performing sequences of actions with varying degrees of autonomy.
The company's report identifies risks including prompt manipulation, exposure of sensitive information, compromised identities and privileges, excessive agent permissions, and tampering with configurations, memory or supply chains.
This matters because an AI agent connected to business systems may be able to do considerably more than a conventional chatbot. If its credentials or instructions are compromised, the systems and data it is authorised to access can potentially become part of the attack surface.
Microsoft cites industry projections suggesting roughly 1.3 billion AI agents could be operating in production environments by 2028.
Humans and Stolen Credentials Remain Major Weaknesses
Despite the growing attention around autonomous AI attacks, Microsoft's data shows that traditional security weaknesses remain highly important.
People and identities continue to provide attackers with major initial-access opportunities. Phishing, impersonation, user execution and compromised accounts remain effective techniques.
Microsoft says it detected more than 46 million business-contact impersonation attacks over the previous 12 months. It also recorded more than 145 million QR-code phishing attacks between July 2025 and June 2026 through Microsoft Defender for Office 365.
Among observed intrusions involving valid accounts, 52.2% involved subsequent credential theft, demonstrating how one compromised identity can potentially provide a path toward additional accounts and systems.
AI Is Becoming a Target as Well as an Attack Tool
The risk is moving in both directions.
Cybercriminals can use AI to attack conventional systems, but AI platforms themselves are also becoming targets.
Microsoft says attackers may attempt to manipulate prompts, steal model-related data, compromise infrastructure, extract sensitive information or abuse computing resources.
The company highlighted a December 2025 case involving a malicious browser extension with more than 600,000 installations that harvested ChatGPT and DeepSeek conversation histories. Microsoft says the activity affected almost 10,000 organisations before being mitigated.
Such incidents illustrate why AI security extends beyond protecting the underlying model. Organisations also have to secure credentials, connected tools, stored conversations, data permissions and surrounding infrastructure.
Governments Are Among the Most Heavily Affected Sectors
Microsoft's report found that government agencies and services represented 27% of observed cyber-threat activity affecting the sectors it tracked in 2026, up from 17% in 2025.
Government networks can be attractive targets because they hold sensitive information, operate essential services and connect with contractors, technology providers and critical infrastructure.
Microsoft also found that research and academia accounted for 38% of observed attacks across the state and local government, education and critical-infrastructure grouping it analysed from November 2025 through April 2026.
AI Is Also Helping Cyber Defenders
The picture is not entirely one-sided.
The same capabilities that allow attackers to automate reconnaissance or analyse vulnerabilities can help defenders identify malicious activity, correlate security signals and respond faster.
Microsoft says organisations using its Security Copilot report threat summarisation that is 60% to 70% faster, helping reduce the time needed to resolve critical alerts. Because this figure comes from Microsoft and relates to its own security product, it should be understood as a company-reported result rather than an independent industry-wide benchmark.
Microsoft's broader argument is therefore not simply that “AI makes cyberattacks worse.” It is that both attackers and defenders are gaining automation capabilities, creating a contest over who can detect, decide and respond faster.
Why Microsoft's Warning Matters
AI changes cybersecurity primarily by affecting speed, scale and accessibility.
Tasks that once required specialist knowledge can increasingly receive assistance from AI models. At the same time, experienced attackers can use automation to perform established techniques more efficiently.
For defenders, that reduces the amount of time available between discovery of a weakness and attempts to exploit it.
But Microsoft's evidence also provides an important reality check: many successful attacks still depend on familiar weaknesses such as compromised identities, excessive privileges, phishing and unpatched internet-facing systems.
Consequently, AI security does not replace conventional cybersecurity. Organisations still need strong identity controls, phishing-resistant authentication, least-privilege access, rapid vulnerability remediation, monitoring and secure software development.
The Cybersecurity Race Is Moving Toward Machine Speed
Microsoft's 2026 findings point toward a security environment in which both sides increasingly use AI.
Attackers can automate parts of vulnerability discovery, social engineering and intrusion workflows. Defenders can use the same technological shift to analyse huge quantities of security data and accelerate investigation and response.
The long-term outcome is therefore not predetermined. AI gives cybercriminals additional capabilities, but it also provides defenders with new tools.
Microsoft's warning is ultimately about the shrinking response window: as cyber operations accelerate, organisations may increasingly need security systems capable of detecting and responding to threats at comparable speed.